Granular Access
Control access by user, group, storage repository, folder, or individual file.
Government & Defense
Extend Zero Trust directly to CUI and sensitive information across government, defense, and contractor environments.
FileFlex Enterprise provides granular Zero Trust Data Access to sensitive information across existing on-premises, cloud, SharePoint, file server, NAS, and legacy infrastructure—without requiring data migration or disrupting established workflows.
Request a Government & Defense Demonstration ›The Missing Layer of Zero Trust
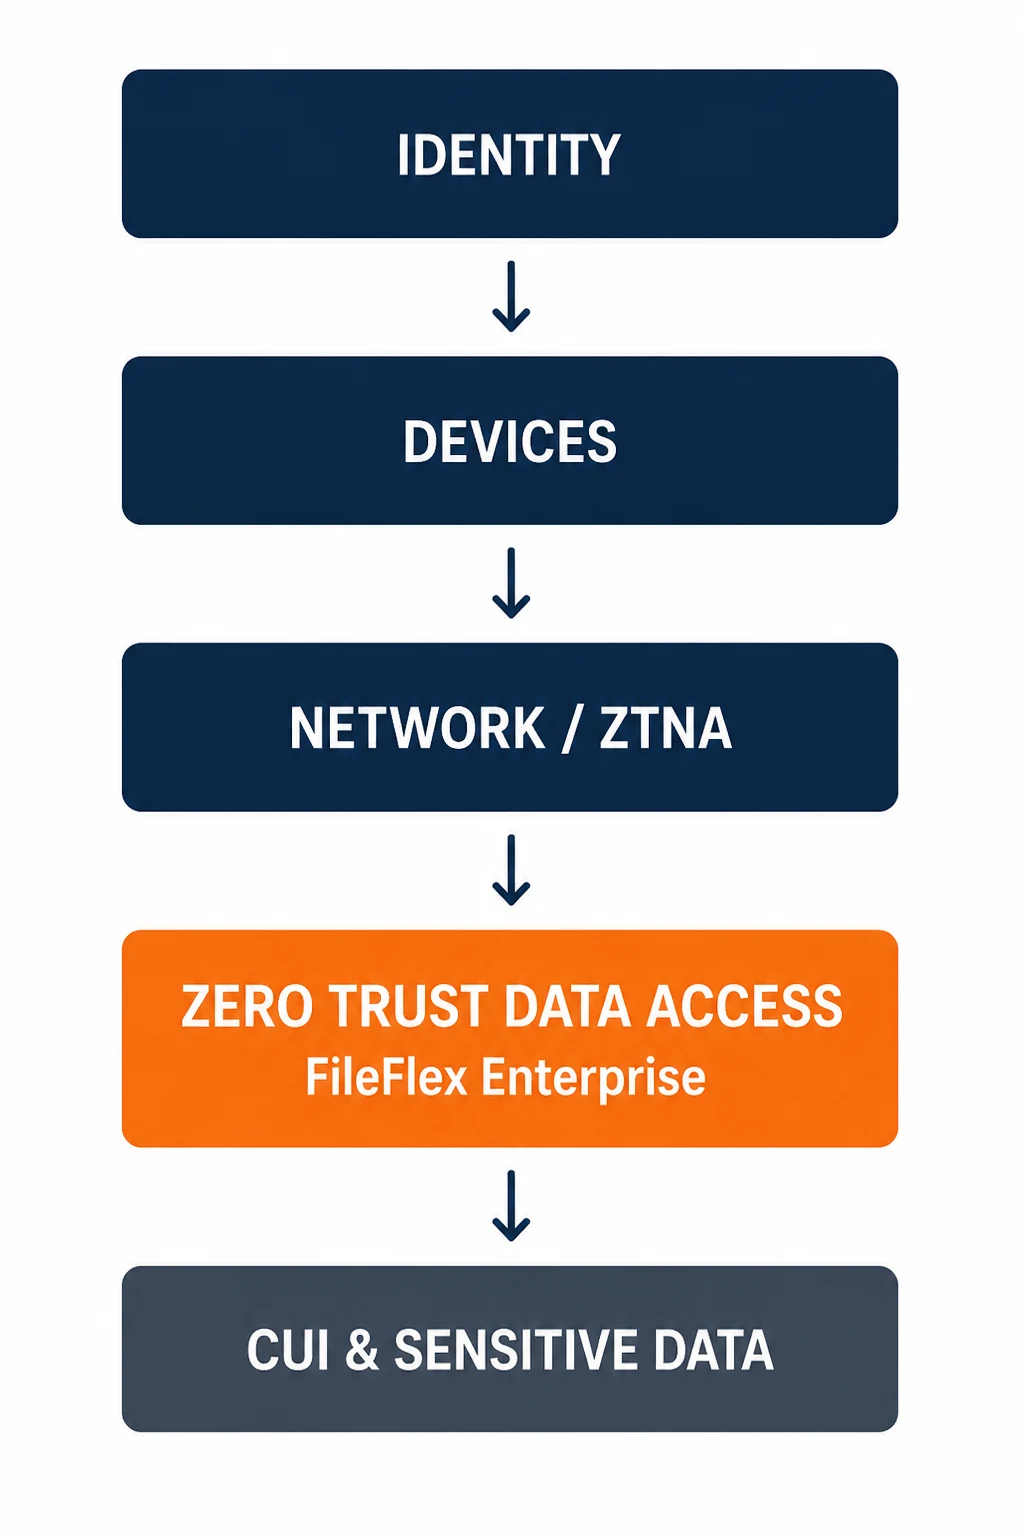
Government agencies and defense contractors have invested heavily in identity security, MFA, endpoint protection, network segmentation, ZTNA, and other Zero Trust technologies.
But the information these systems are ultimately designed to protect—Controlled Unclassified Information (CUI), engineering files, technical documentation, contracts, operational records, and other sensitive unstructured data—remains distributed across file servers, NAS systems, SharePoint, cloud storage, FTP servers, and legacy infrastructure.
Traditional Zero Trust technologies protect identities, devices, applications, and network connections.
FileFlex Enterprise extends Zero Trust to the data layer.
It applies granular, policy-based controls directly to access to files and folders, helping government and defense organizations protect sensitive information wherever it resides.
Protect Controlled Unclassified Information
Government agencies, defense organizations, prime contractors, subcontractors, and other members of the Defense Industrial Base need to provide authorized users with access to Controlled Unclassified Information without unnecessarily exposing the systems where that information resides.
FileFlex Enterprise applies granular access controls directly to CUI and other sensitive information while allowing the data to remain within existing government or contractor-controlled infrastructure.
Control access by user, group, storage repository, folder, or individual file.
Govern whether authorized users can view, edit, download, upload, or share information.
Provide secure access without migrating or duplicating information into another content repository.
Maintain detailed activity logs of access and sharing activity across protected information.
Apply consistent access policies across distributed on-premises, cloud, and hybrid environments.
Modernize Without Migration
Government and defense environments rarely operate from a single storage platform.
Sensitive information may be distributed across data centers, facilities, file servers, NAS systems, SharePoint, cloud infrastructure, FTP servers, and legacy systems accumulated over many years.
Replacing or consolidating that infrastructure can introduce cost, complexity, operational disruption, and risk.
FileFlex takes a different approach.
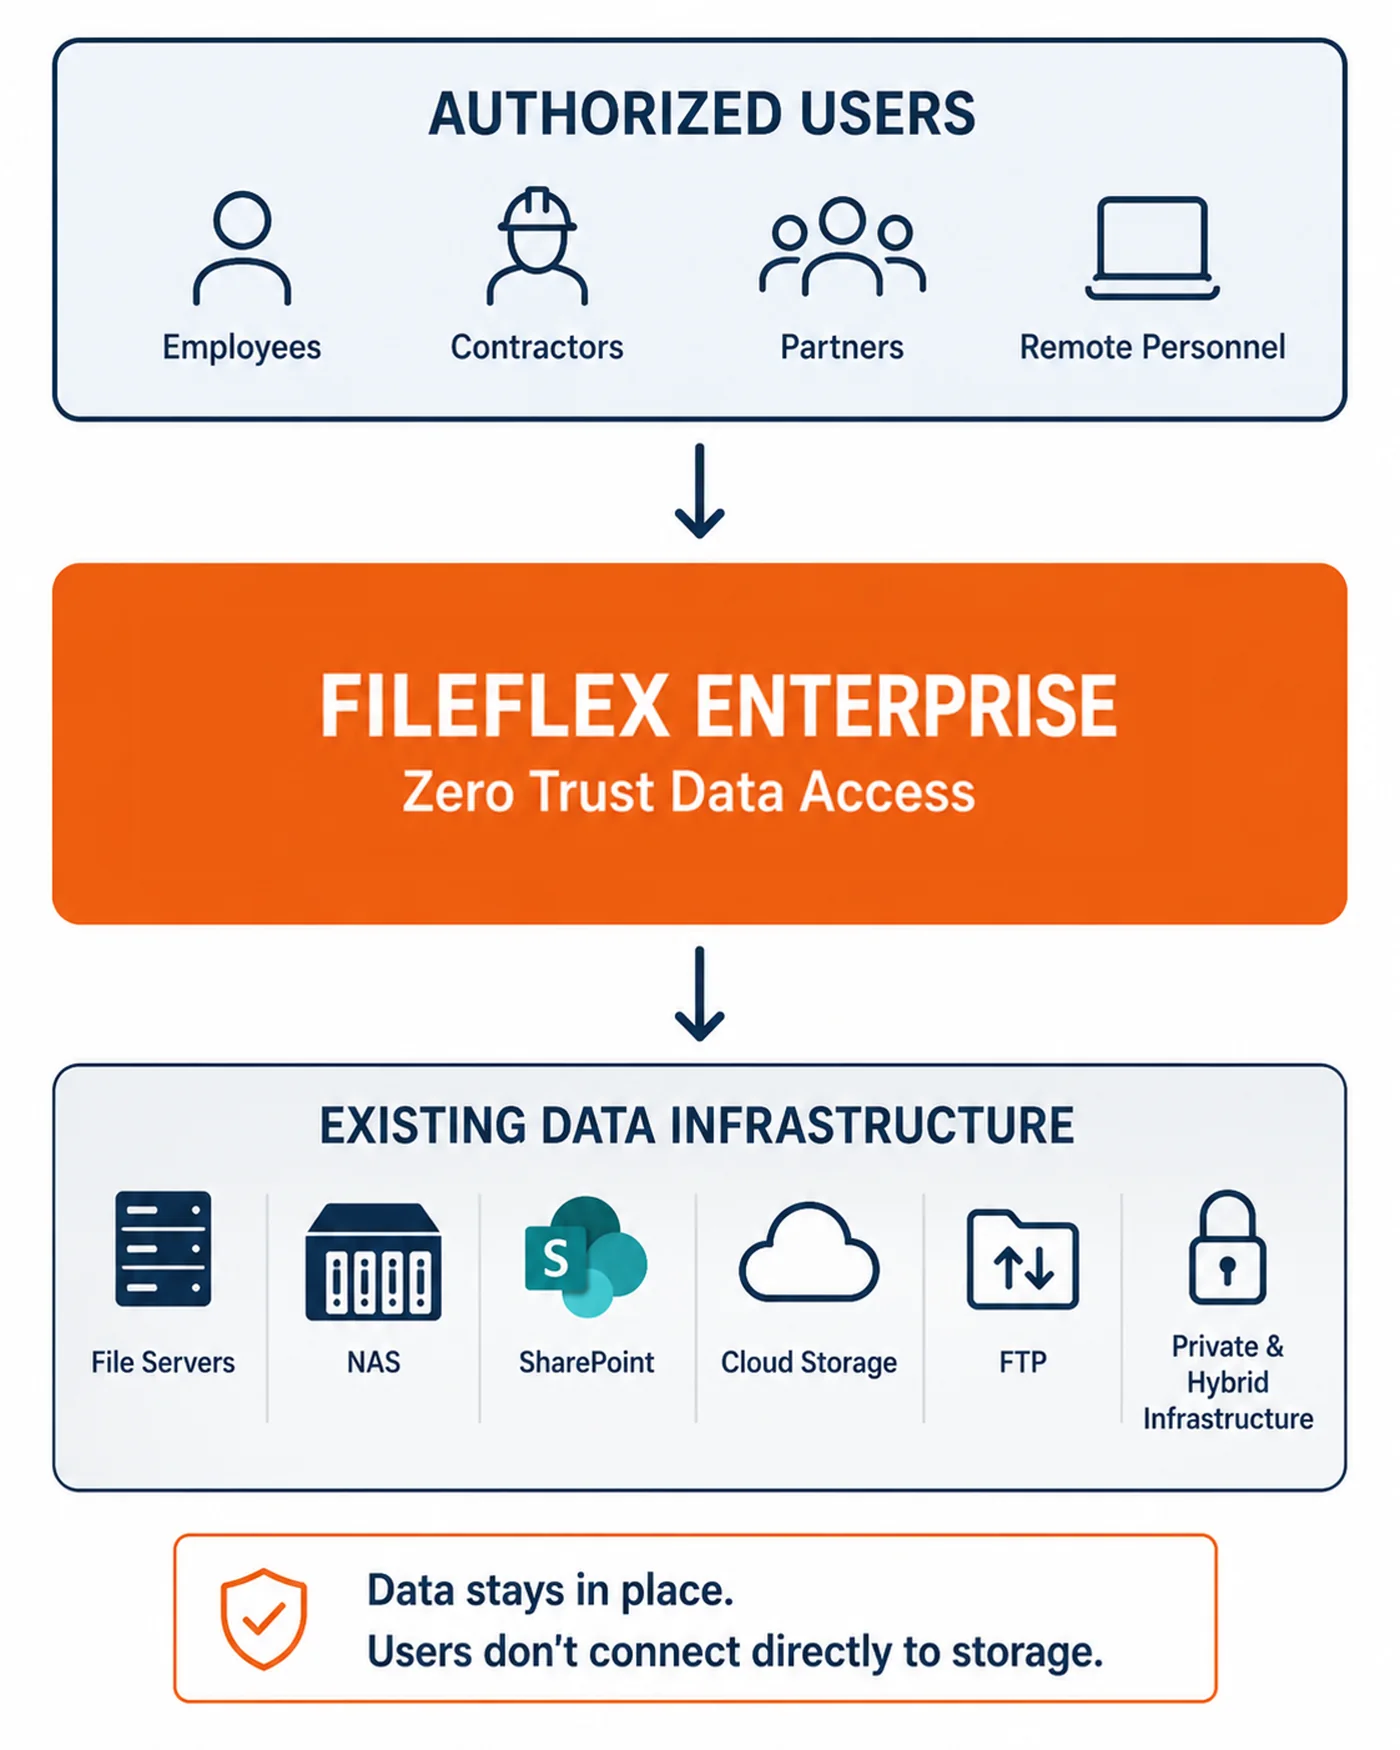
FileFlex Enterprise overlays existing infrastructure with a common Zero Trust Data Access layer, allowing organizations to strengthen security and governance without replacing the systems that already store their information.
Secure Access by Design
Users do not connect directly to the underlying storage repositories. FileFlex mediates access requests and applies policy before authorized information is retrieved.
FileFlex Connector Agents operate behind the firewall using outbound HTTPS connections, eliminating the need to open inbound firewall ports to storage infrastructure. Customer files remain within the organization's existing storage environment rather than being moved into FileFlex.
Controlled Cross-Boundary Access
Government and defense information frequently needs to cross organizational boundaries.
Employees, contractors, subcontractors, suppliers, partners, and other authorized third parties may all require access to sensitive information—but they do not all require access to the networks and storage systems where that information resides.
FileFlex enables organizations to provide controlled access to the information people need while maintaining governance over the underlying data.
Provide employees and authorized remote personnel with secure access to the information they need.
Enable controlled access to CUI and sensitive project information across prime contractors, subcontractors, suppliers, and other authorized DIB participants.
Provide narrowly scoped access to specific files and folders without broadly exposing internal networks or storage repositories.
Create controlled environments for procurement, regulatory review, investigations, projects, and other sensitive collaboration without moving information into another repository.
Govern Distributed Environments
Government and defense organizations frequently operate across multiple departments, facilities, programs, contractors, and administrative domains.
FileFlex enables central IT and security teams to establish consistent access policies and maintain visibility while supporting granular administration of access to individual users, groups, repositories, folders, and files.
Central policy. Local administration. Granular data access.
At the same time, FileFlex helps reduce unnecessary exposure by separating users from the underlying storage infrastructure and limiting access to the information they are authorized to use.
Technical Controls for Broader Programs
FileFlex Enterprise provides technical capabilities that can support broader government and defense cybersecurity and compliance programs by strengthening access control, least privilege, secure data access, activity visibility, and controlled external collaboration.
FileFlex can help Defense Industrial Base organizations implement technical controls relevant to protecting CUI, including granular access control, least privilege, controlled remote access, and activity logging.
FileFlex supports organizations implementing access-control and accountability practices designed to protect CUI within non-federal systems and environments.
FileFlex extends Zero Trust principles beyond identity and network access by applying policy-based controls directly to access to files and folders.
FileFlex can provide Zero Trust Data Access to information residing within appropriately configured government cloud and hybrid environments.
Purpose-Built Data Access Security
Extend Zero Trust principles directly to access to sensitive files and folders.
Strengthen control over sensitive information without requiring wholesale storage replacement or data migration.
Limit users to the specific repositories, folders, and files they are authorized to access.
Sensitive files remain within existing government or contractor-controlled storage infrastructure.
Apply a common access layer across cloud, on-premises, and legacy storage systems.
Provide contractors, subcontractors, partners, and other authorized users with granular access without broadly exposing internal infrastructure.
Complete Your Zero Trust Architecture
Government Zero Trust strategies have made significant progress securing identities, devices, applications, and networks.
But ultimately, those technologies exist to protect something more important:
The Data.
FileFlex Enterprise extends Zero Trust directly to CUI and other sensitive government information, providing granular control over who can access data and what they can do with it—while allowing that information to remain within existing infrastructure.
Request a Government & Defense Demonstration ›